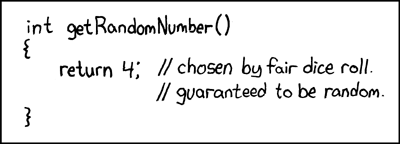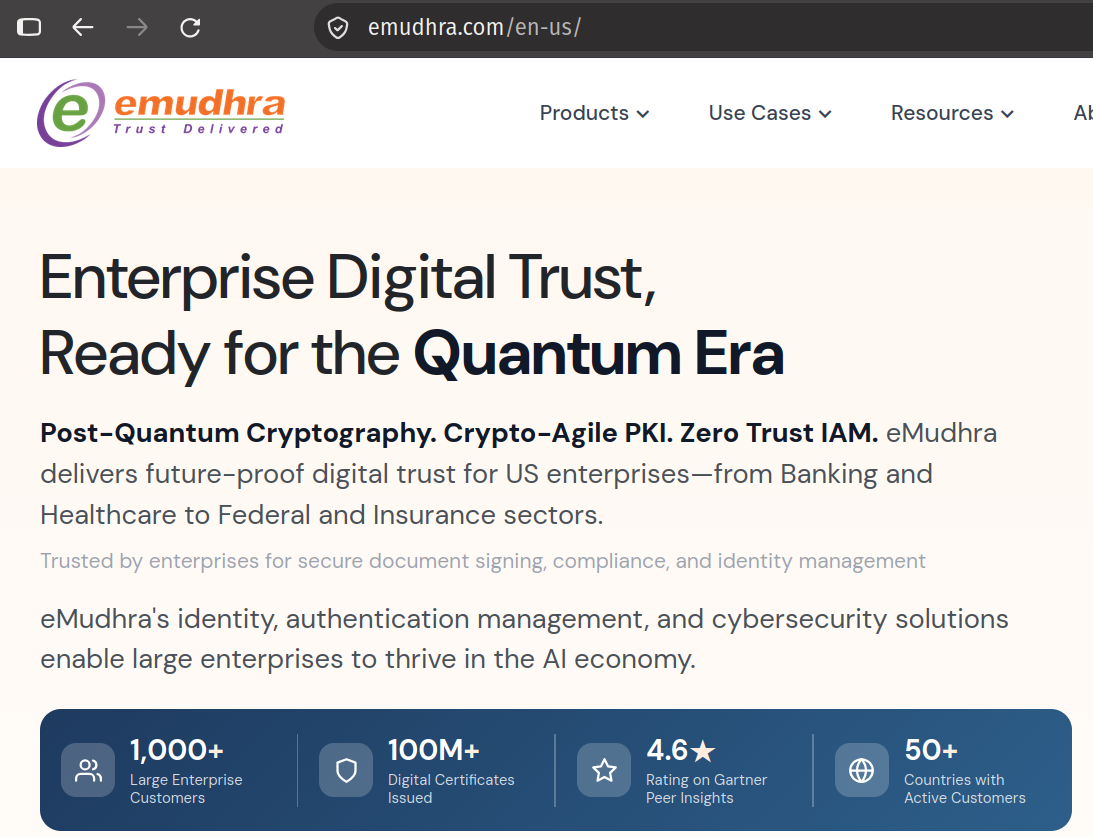
Oh, ze kwamen erachter. Private keys als 4 of 56, ready for the Quantum Era op de SSL certificaten.
RMFAO
Erger is dat ze een hoge rang hadden/hebben in de certificate chain, dus je zou met een geforged certificaat nieuwe certificaten kunnen signeren.
This wasn’t just an embarrassing collection of numbers, either: The weak keys belonged to eight intermediate certificate authorities, potentially allowing attackers to forge certificates trusted by systems that hadn’t blocked them. eMudhra, however, maintains that the affected CAs had issued no end-entity certificates.
The reg